Is Your IAM Ready for AI Agents? Why Secure AI Adoption Starts with Effective Data Access
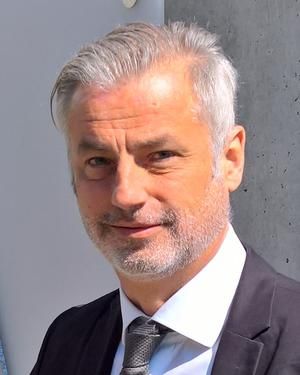
Holger Moenius
Senior AE at CyberDesk
25+ years selling enterprise security across DACH
holger.moenius@cyberdesk.app
Last updated: 06 November 2026 • 8 mins Reading Time
Key takeaways
- Every AI agent is an identity, and every identity carries access. In Microsoft 365, Copilot acts on behalf of a user, and custom agents call Microsoft Graph through app registrations and service principals.
- Agents inherit effective access, not intended access. Effective access is the sum of every group, sharing link, inheritance rule and permission that applies to an identity.
- Dormant oversharing becomes live risk. Agents search systematically and at machine speed, so files shared too widely years ago become reachable.
- Secure AI adoption has one shared prerequisite: an accurate picture of what every human and non-human identity can actually reach.
- The path is discover, structure, enforce: make effective access visible, shrink it to what is needed, then make guardrails decide and log their decisions.
Why do AI agents create a new identity risk?
AI agents turn unused access into exposed access. 95% of permissions are unused. For years, that excess sat dormant because nobody went looking, where agents now inherit.
Four things change when agents join the workforce:
- Faster: AI shortens the time from vulnerability to exploit, so excess access is found and abused sooner.
- At scale: lower barriers to entry let more attackers operate with increasing automation.
- Wider: every AI system and agent adds a new identity, and with it a new path to sensitive data.
- Systematic: agents search exhaustively, surfacing oversharing that went unnoticed for years.
Authorised is not the same as needed. AI guardrails can only decide correctly if they know who and what can actually reach which data.
Where does access drift from intent in Microsoft 365?
Access drifts furthest in five places, and each one becomes an AI exposure path:
- Nested groups, Teams and guests: access arrives through layers nobody reviews directly, and Copilot surfaces all of it.
- SharePoint and OneDrive broken inheritance: project exceptions outlive the project, so agents see the exception, not the policy.
- “Anyone” and organisation-wide links that never expire: forgotten files become reachable the moment an agent searches the tenant.
- Service principals and Graph app permissions: broad, tenant-wide grants form the access supply chain behind every AI integration.
- Orphaned agents and non-human identities: an identity without an owner is an identity without oversight.
Which regulations expect evidence of AI agent access?
NIS2, DORA, the EU AI Act, ISO/IEC 27001:2022, GDPR and the Swiss revFADP all ask the same thing in different words: who accessed what, why, and who was accountable. The whitepaper maps each framework to the evidence it expects, including Germany’s NIS2UmsuCG, in force since 6 December 2025 with personal liability for management.
With AI agents multiplying and regulations like NIS2, DORA and the EU AI Act raising the bar, how do we secure AI adoption without slowing it down?
What’s inside the whitepaper?
- The five foundations for secure AI adoption
- Eight best practices for identity, access and AI guardrails
- A regulation-by-regulation evidence map for NIS2, DORA, EU AI Act, ISO 27001, GDPR and revFADP/FINMA
- A 180-day roadmap from visibility to enforceable guardrails
Ready to see who and what can reach your data?
Download the whitepaper to learn how to baseline effective access, close the gaps AI agents expose, and scale Copilot without data-exposure concerns blocking your rollout.
Frequently asked questions

Founders
Dr. Tobias Lieberum & Prabhakar Mishra
Year of foundation
2022
Headquarters
Munich, Germany

Get in touch with us
Headquartered in Munich, Germany.
Partners

Copyright © CyberDesk GmbH 2026. All rights reserved.